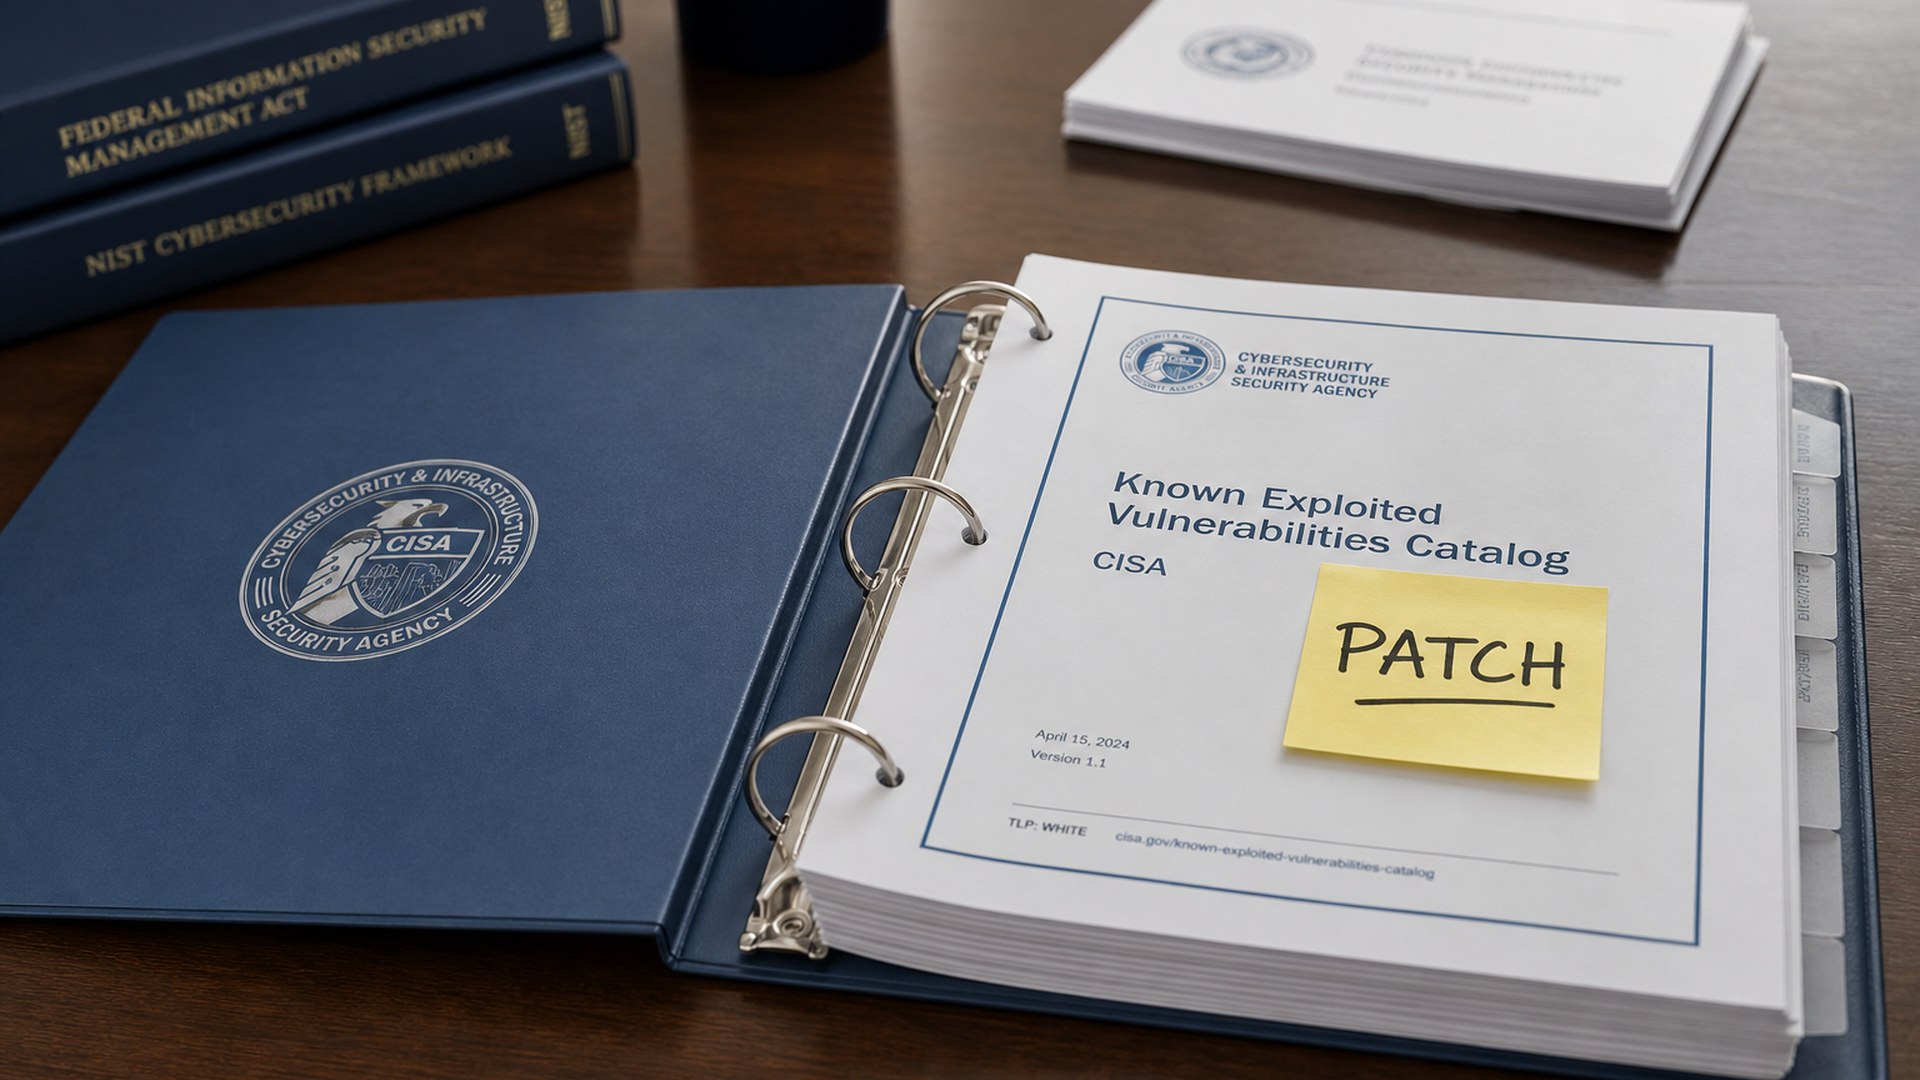
Open the book before you open the ticket. CISA's Known Exploited Vulnerabilities catalog sits at cisa.gov/known-exploited-vulnerabilities. It's a public list. CVE IDs. Vendor and product names. Vulnerability names. Dates added. Required action language. Due dates for federal civilian agencies under Binding Operational Directive 26-04. You're not hunting a lab recipe. You're learning to read a prioritisation file the whole sector can share on the same morning.
Quin Halberg · Sunday 6 September 2026
Read next
Step by step
- Pull KEV or the alert
Load cisa.gov/known-exploited-vulnerabilities and find the newest rows, or pull the KEV JSON feed.
- Match to your estate
Match each CVE and product to your CMDB, SBOM and edge list.
- Assign an owner
Give each match a named owner before standup ends.
- Patch
Patch to the fixed build the vendor names.
- Rotate secrets
Rotate any secrets that might have been touched.
- Check for compromise
Check the logs to see whether the system was quiet before the fix.
- Close the change
Close the change with the CVE string in the ticket title so later audits can find it.
This desk has not corrected this file. Corrections.
The paper
Comments
No notes on this story yet.
Sign in to comment