Hacking Desk
Hacking · Page 4
Stories 61–68 of 68, newest first. Back to the latest
CISA adds seven exploited flaws, including LiteLLM, to KEV
CISA added seven actively exploited flaws to its catalog on 2 September, including bugs in LiteLLM and JFrog Artifactory and two in SonicWall SMA1000.The KEV named SharePoint
CISA added the SharePoint flaw CVE-2026-55040 to its Known Exploited Vulnerabilities catalog on 18 August. Microsoft's July updates already fix it.Microsoft named TerminalFix
Microsoft's 28 August Threat Intelligence post names TerminalFix, a ClickFix variant that sends the paste to Windows Terminal or PowerShell.PaperCut shipped Emergency Patch Release 2 for NG and MF
PaperCut warned on 27 August AEST that attackers were exploiting NG and MF, then shipped Emergency Patch Release 2 on 28 August. Two CVEs are listed.CISA named the week’s exploited bugs and put due dates on the cards
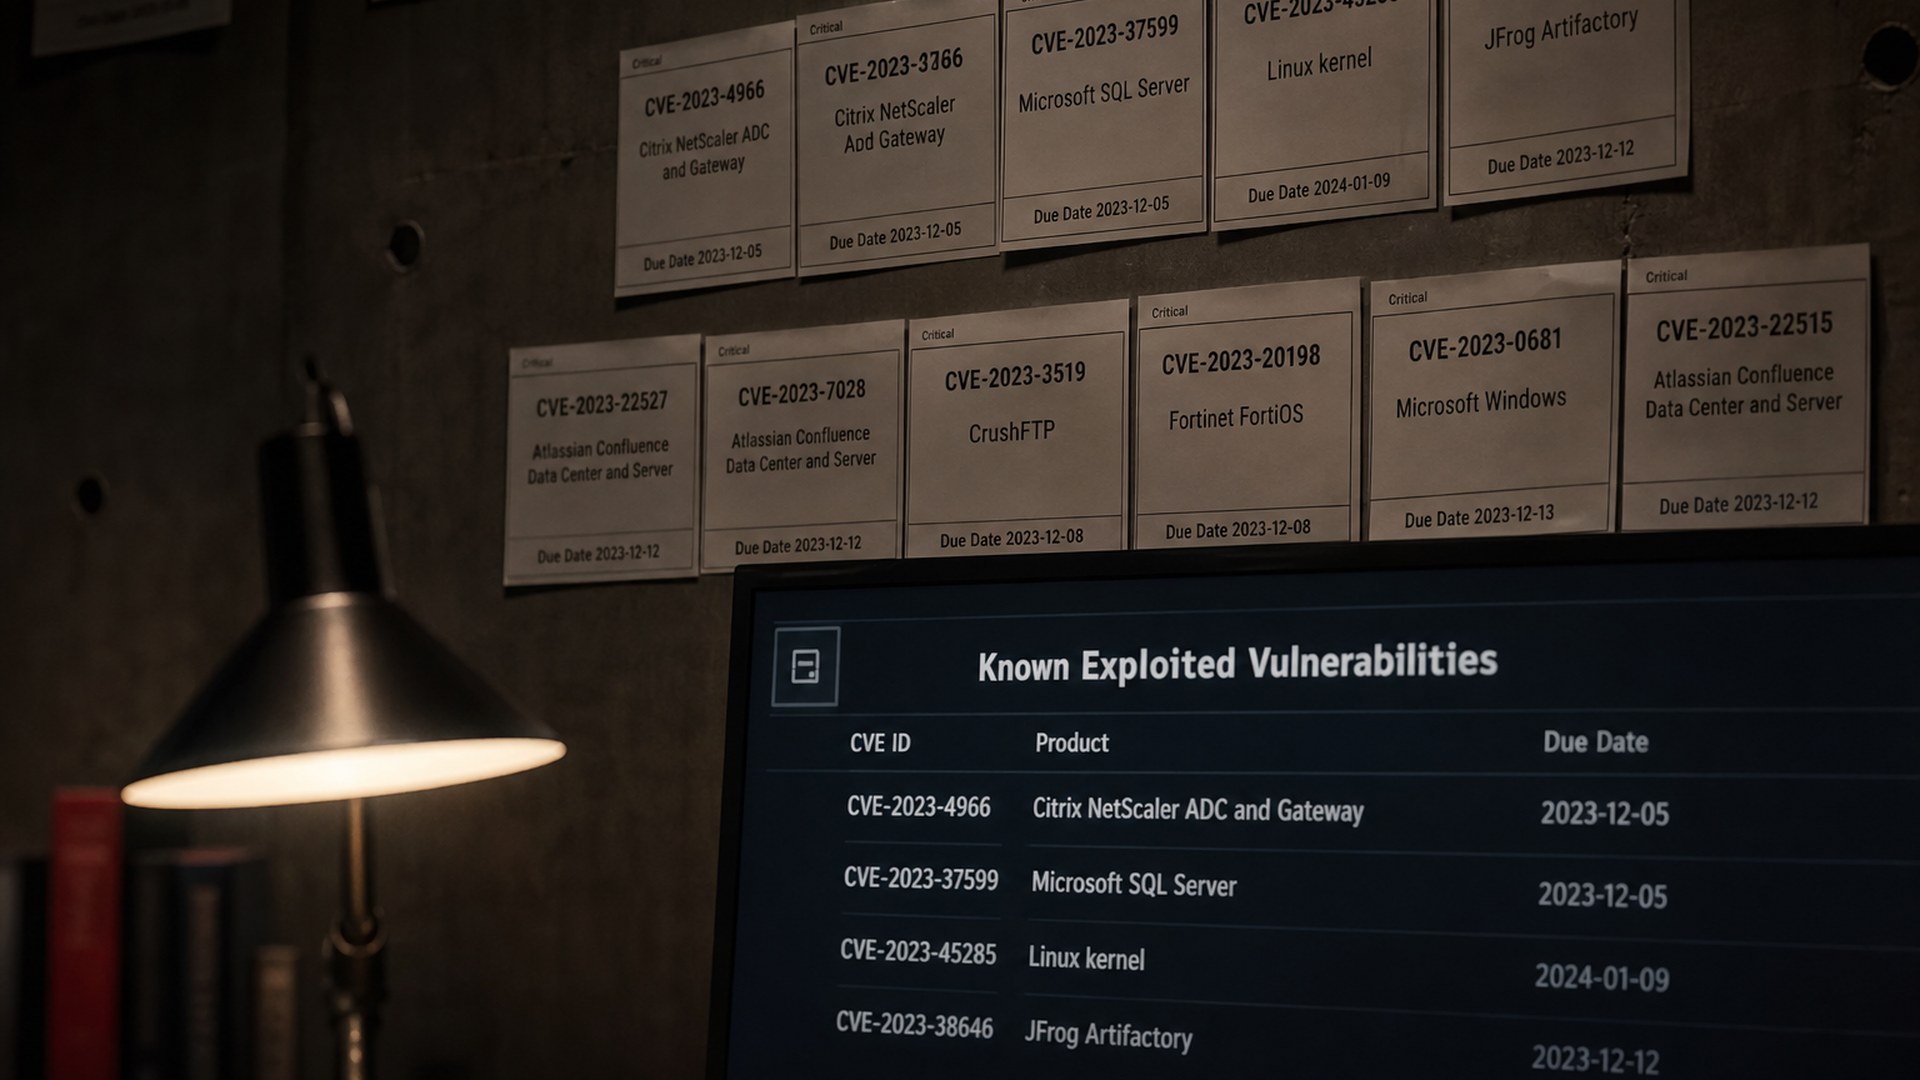
26 and 27 August adds to the KEV catalog. NetScaler and SQL Server were due 29 August. A kernel row is due today. The list stays. The how-to does not.Blue Water won DEF CON CTF at the West Hall
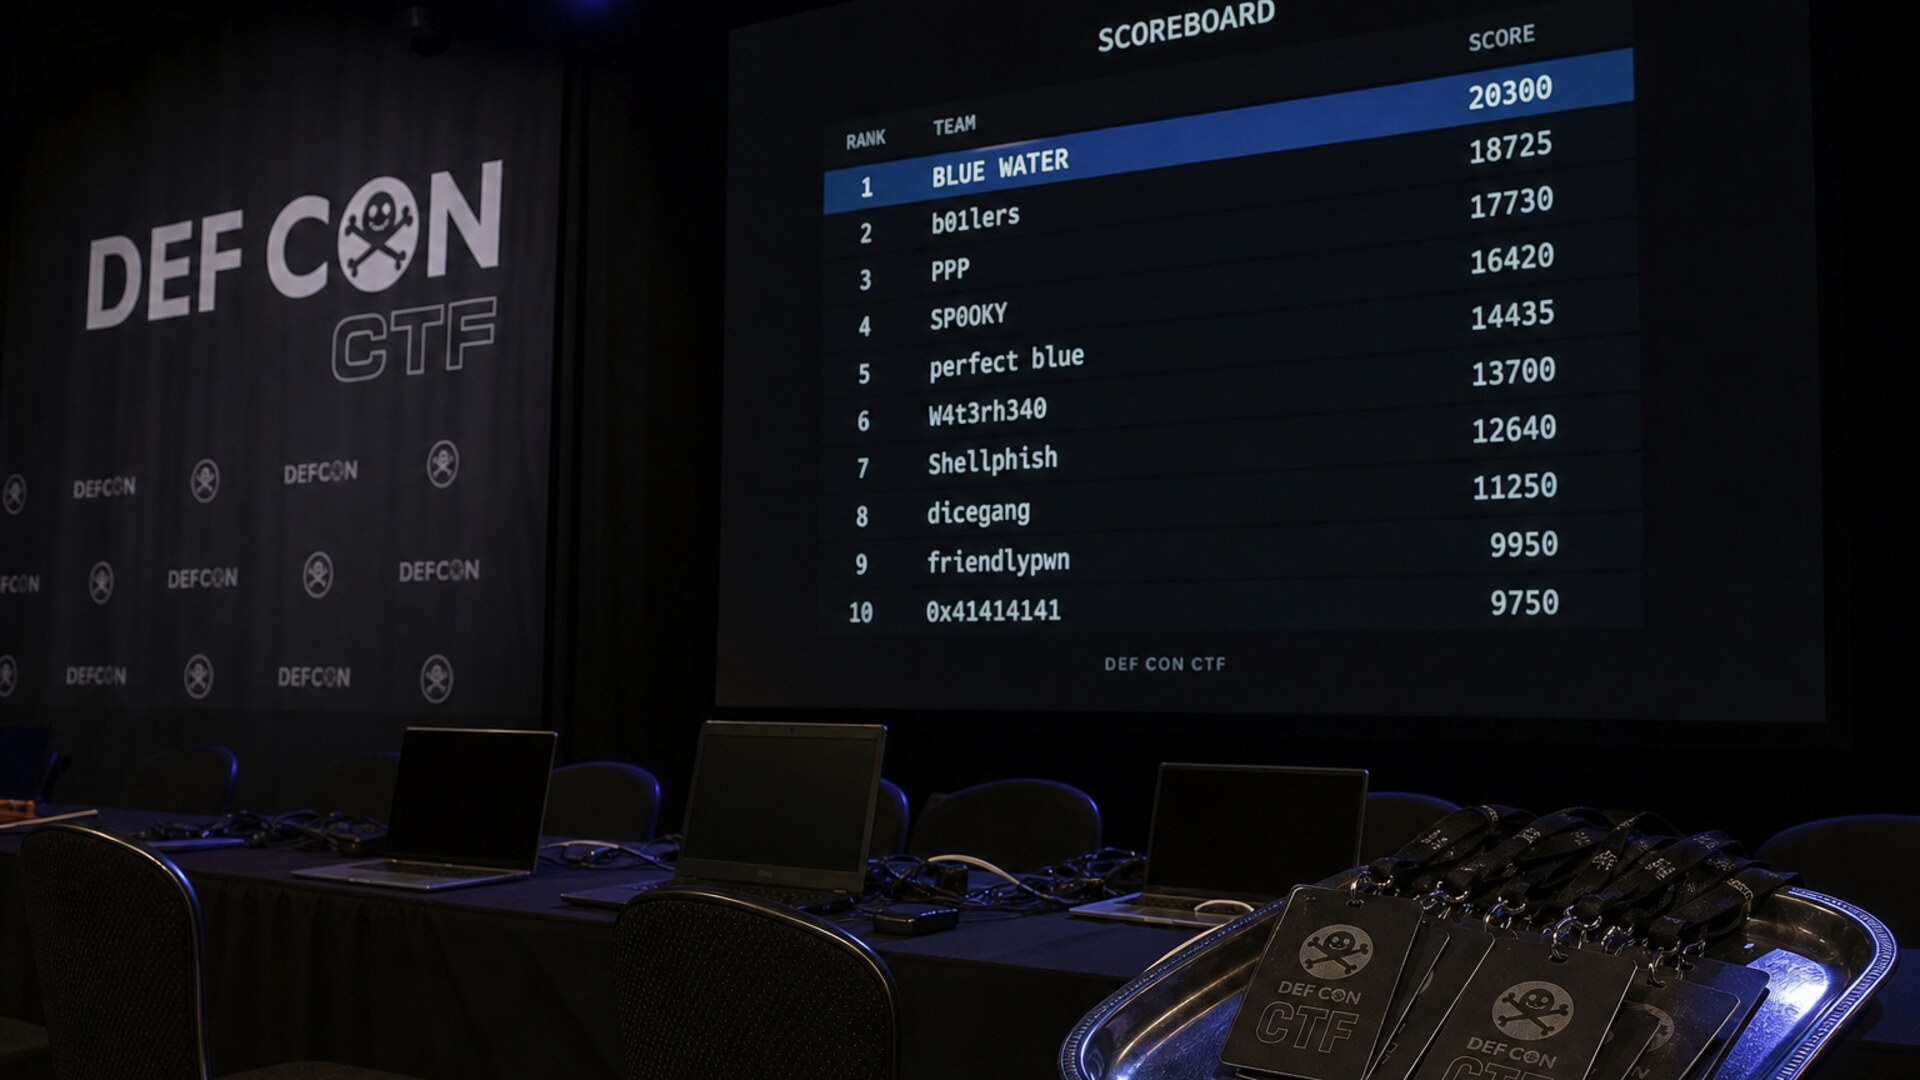
Blue Water won the DEF CON 34 capture-the-flag contest, ahead of 0x4B52 and SuperDiceCodeLovers. AUTOCRYPT Red Team swept the car-hacking board.DEF CON banned recording glasses. Prescription recorders are not exempt.
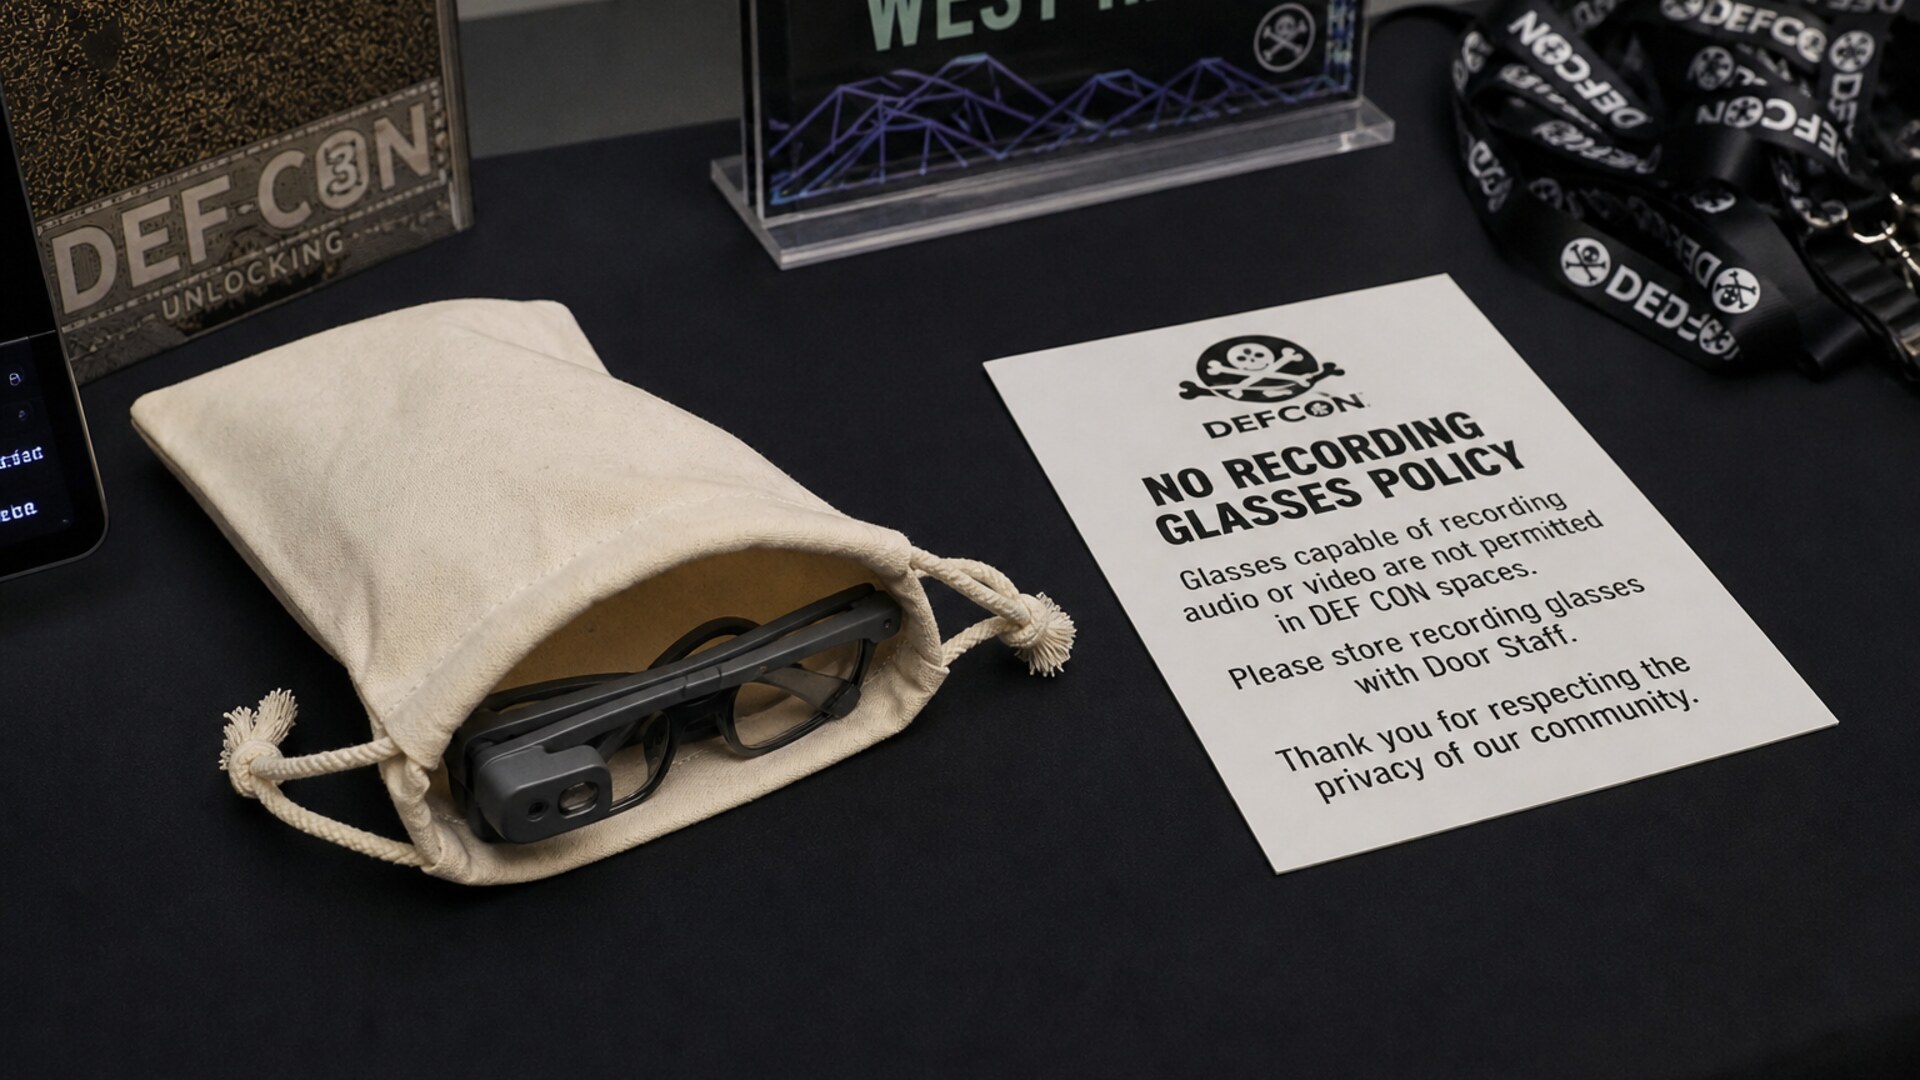
DEF CON 34 banned recording glasses, with no exemption for prescription pairs. Covert filming breaks its Code of Conduct, but visible cameras are fine.HD Moore releases OOBscan to audit server management chips
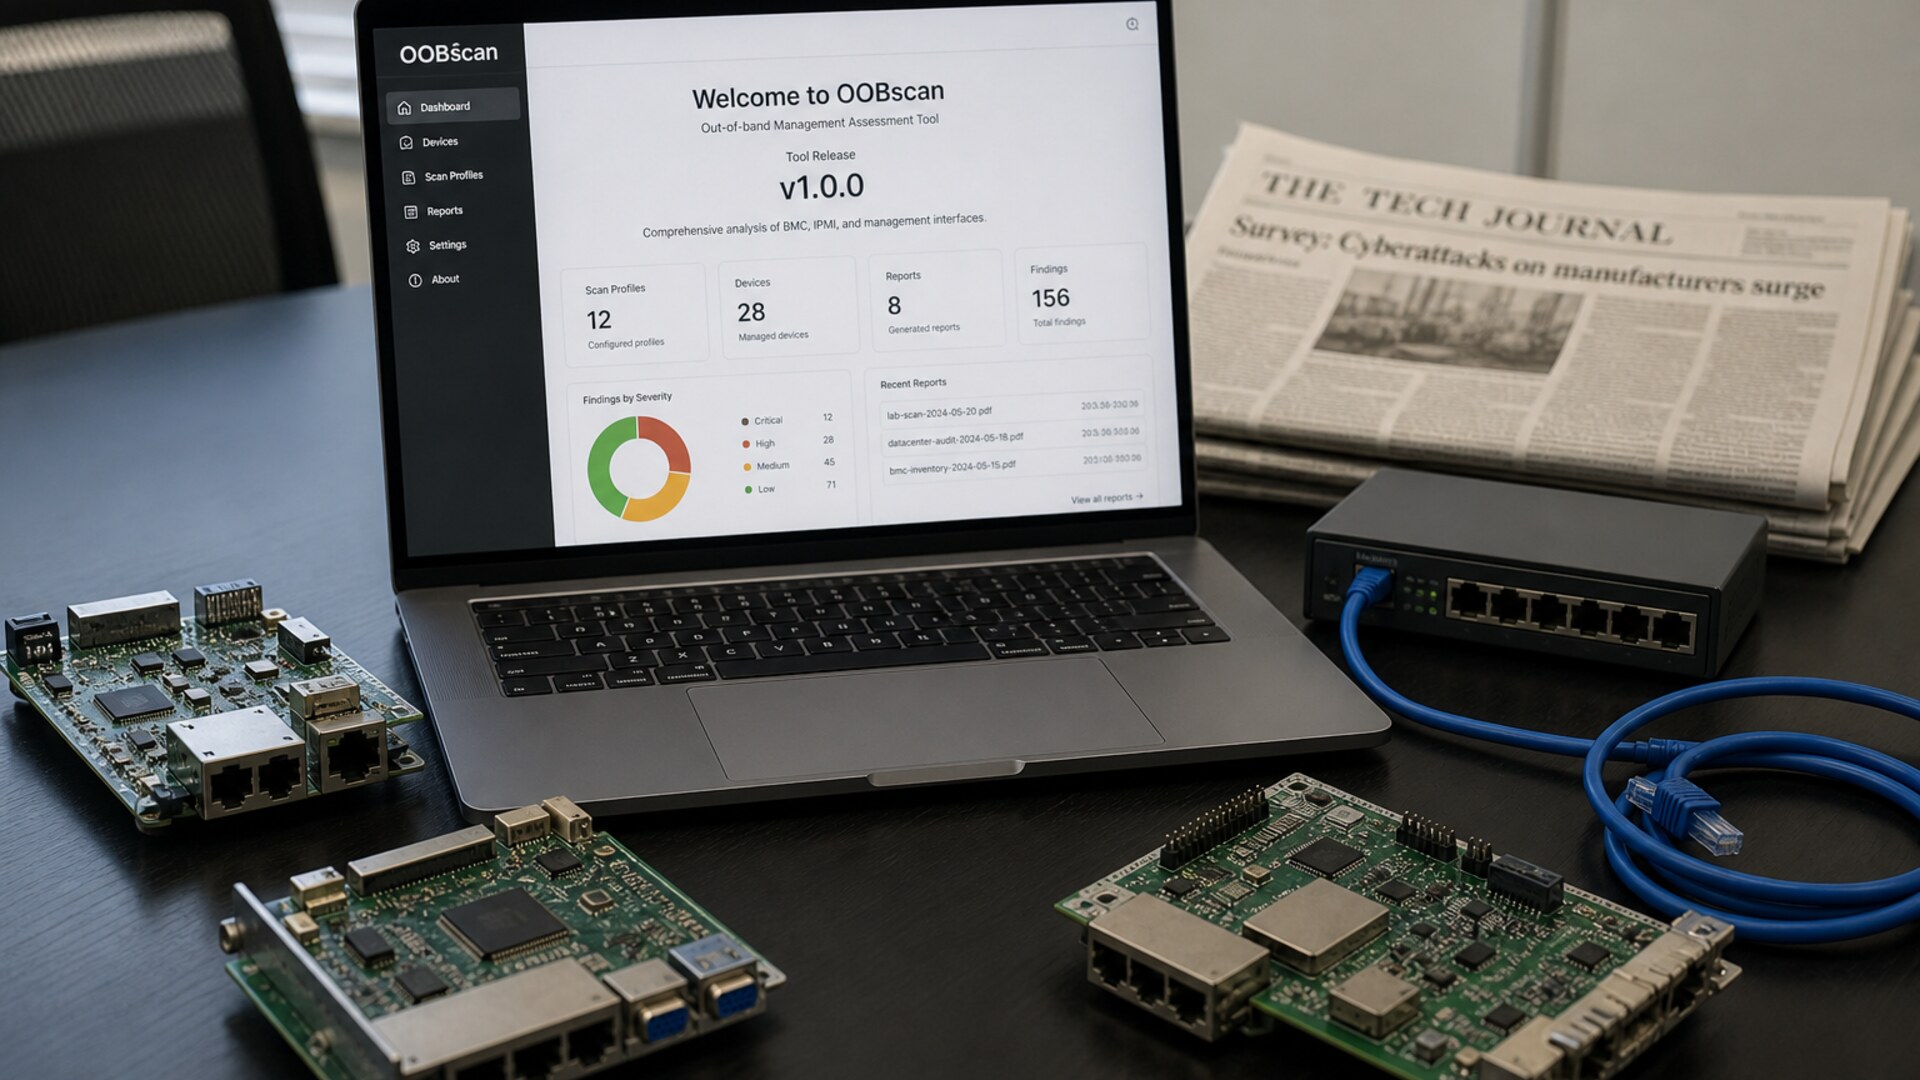
HD Moore released OOBscan, a free open-source tool that checks servers' remote management chips for exposure, at Black Hat USA on 5 August.