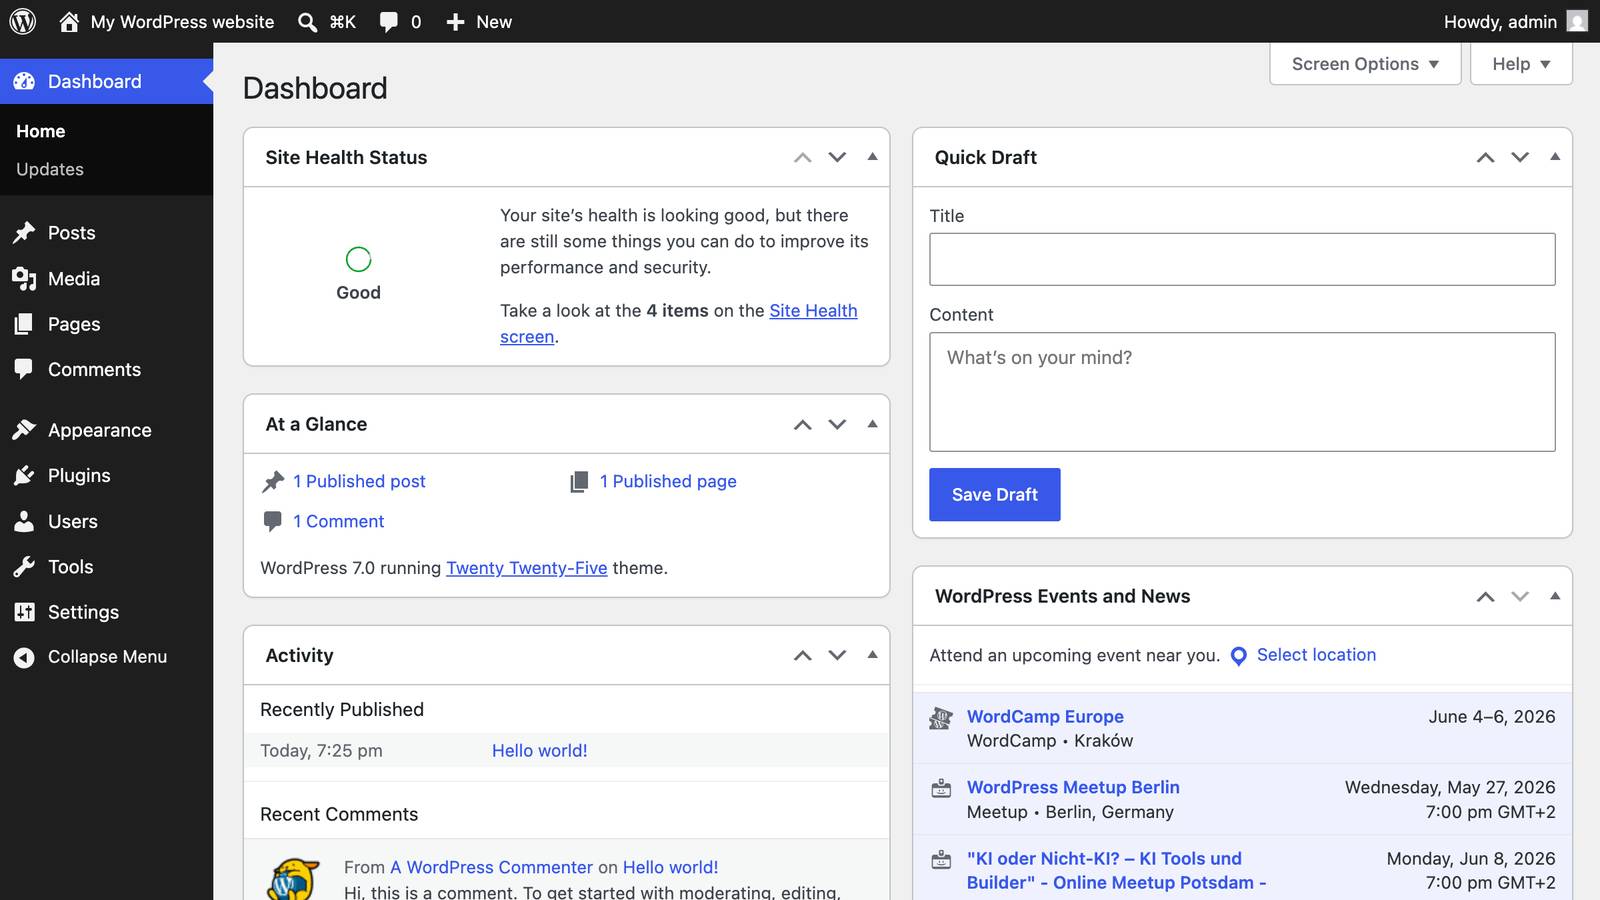
WordPress shipped an emergency security release after researchers found a way for an unauthenticated attacker to pull unexpected PHP files into page-template resolution. Under the wrong theme and server conditions, that becomes remote code execution. The bug is CVE-2026-87902.
Quin Halberg · Saturday 17 October 2026
Read next
This desk has not corrected this file. Corrections.
The paper
Comments
No notes on this story yet.
Sign in to comment