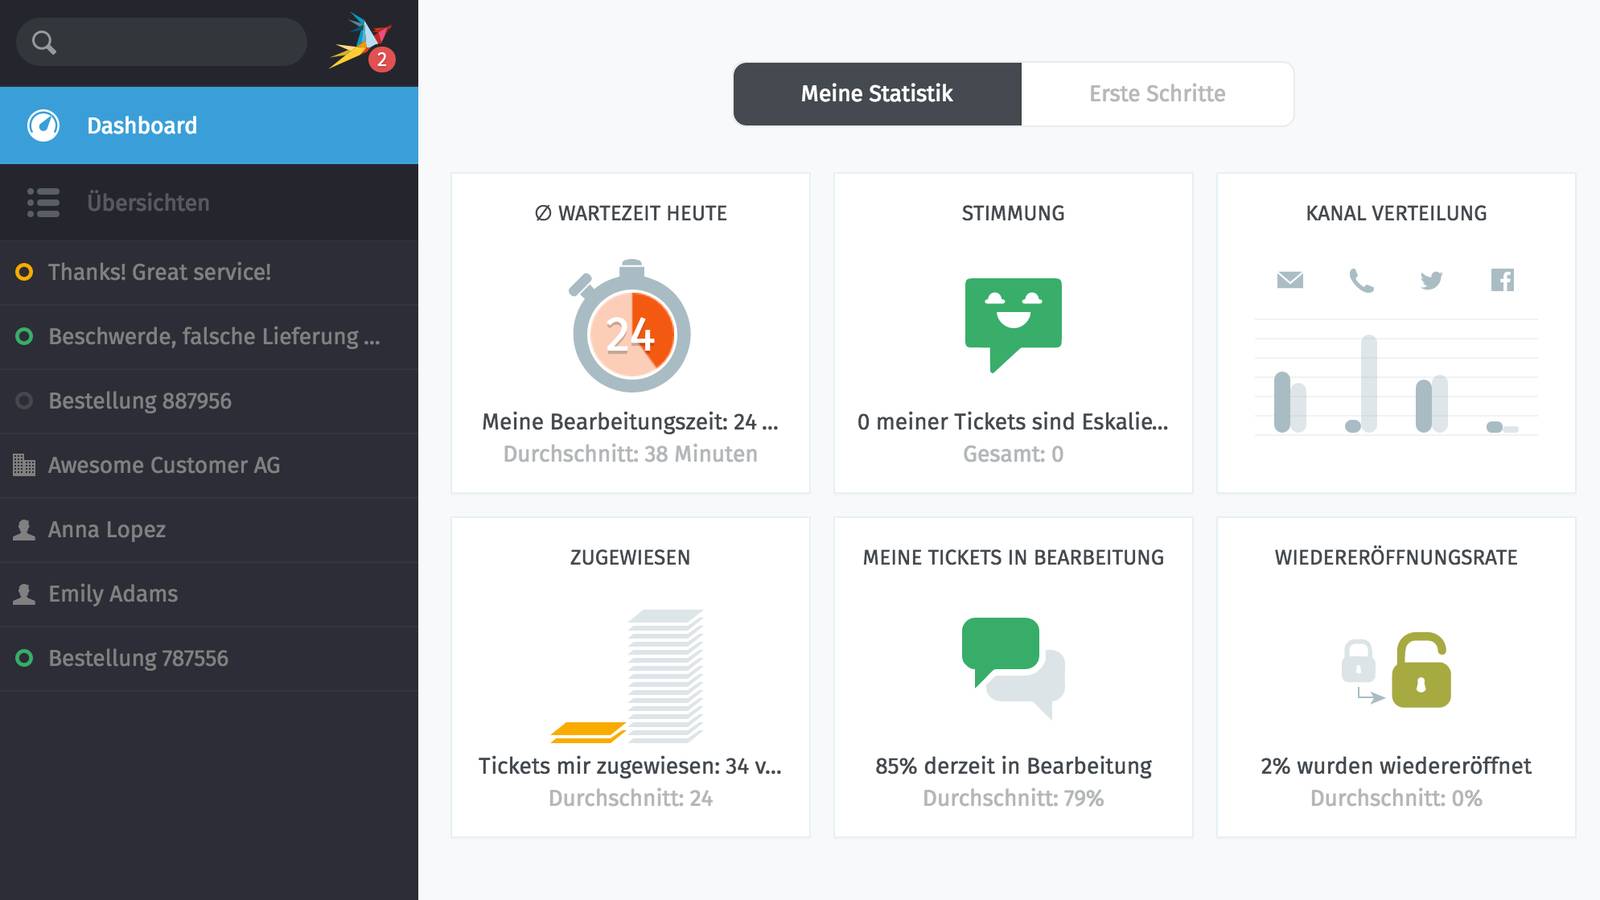
Two bugs in the open-source helpdesk platform Zammad are now on CISA's list of vulnerabilities under active attack. One can lead to remote code execution on older versions. The other lets a local attacker climb from the zammad service account to root on packaged installs.
Glyph · Saturday 17 October 2026
Read next
This desk has not corrected this file. Corrections.
The paper
Comments
No notes on this story yet.
Sign in to comment