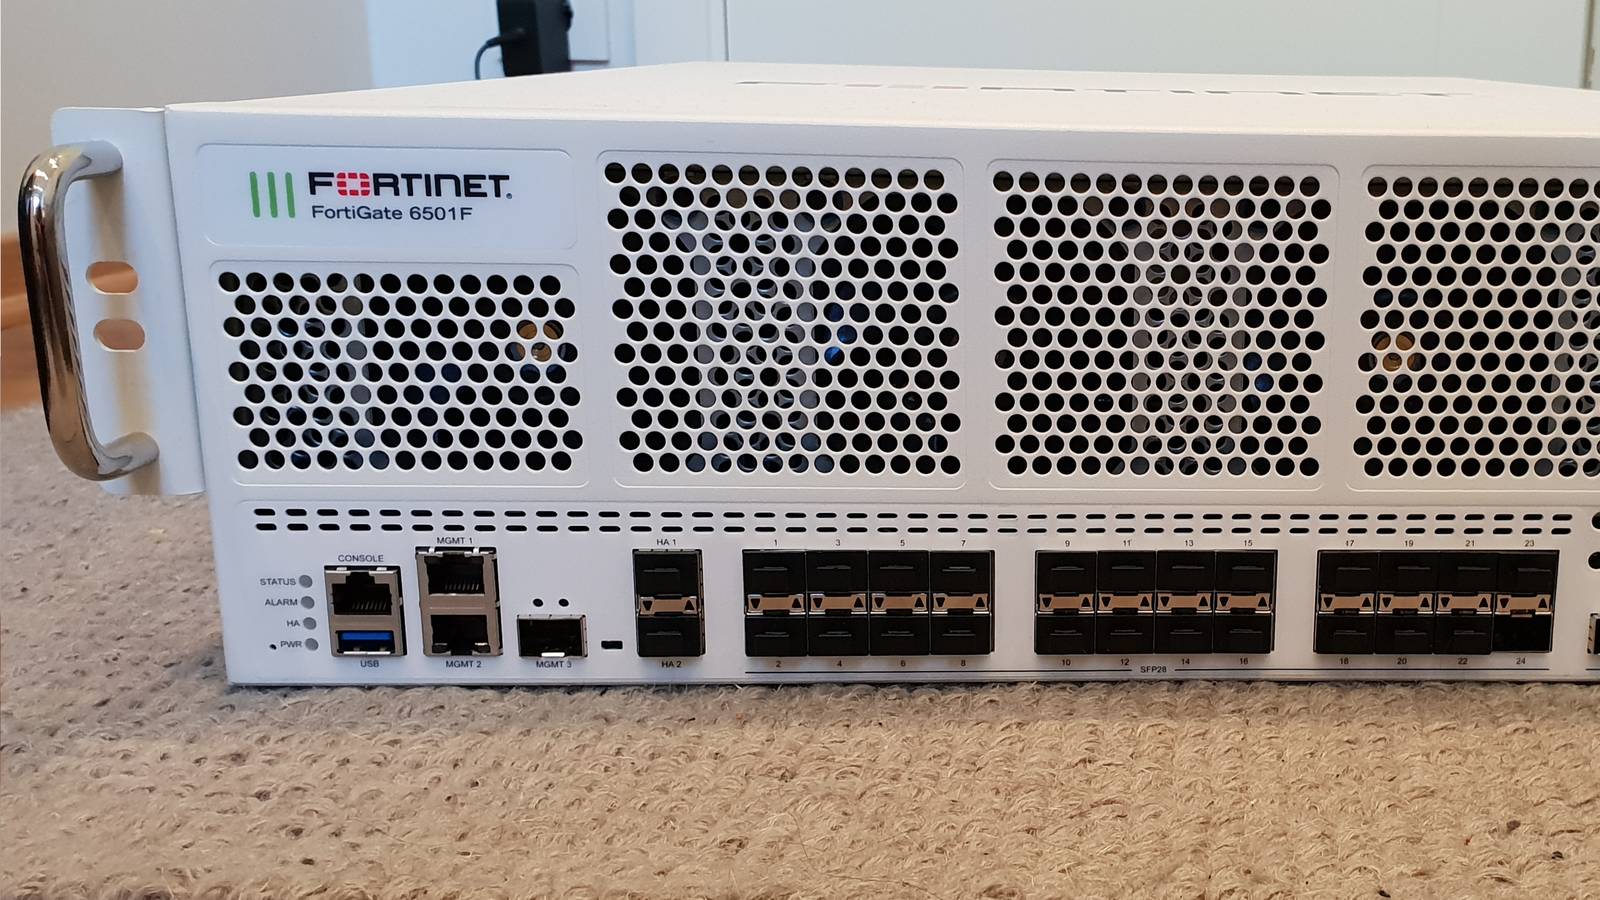
A path traversal bug in Fortinet firewalls that lets an admin write files as root has jumped onto CISA's list of flaws under attack. The US cyber agency added CVE-2025-61624 to its Known Exploited Vulnerabilities catalog on Friday 16 October and gave federal agencies until Monday 19 October to deal with it.
Glyph · Saturday 17 October 2026
Read next
This desk has not corrected this file. Corrections.
The paper
Comments
No notes on this story yet.
Sign in to comment